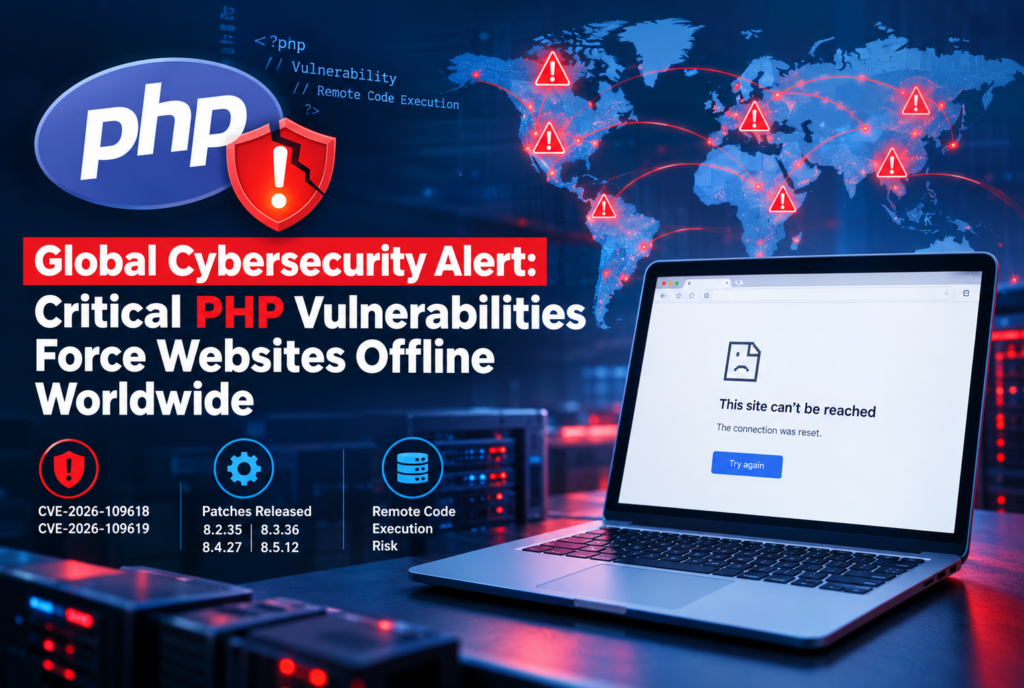
Global Cybersecurity Alert: Critical PHP Vulnerabilities Force Websites Offline Worldwide
October 23, 2026
0
Critical PHP Vulnerabilities Force Websites Offline Worldwide A major cybersecurity alert has put website owners, hosting providers, and IT teams around the world on high alert after two
Critical PHP Vulnerabilities Force Websites Offline Worldwide
A major cybersecurity alert has put website owners, hosting providers, and IT teams around the world on high alert after two critical vulnerabilities were discovered in PHP, a programming language widely used to power websites and web applications. The security flaws have triggered urgent patching efforts, heightened monitoring, and precautionary shutdowns of some online services.
Cybersecurity agencies are urging organizations to identify vulnerable systems and install security updates immediately. Where systems cannot be secured promptly, authorities recommend temporarily isolating them from the internet to reduce the risk of exploitation.
What Happened in the Global PHP Security Alert?
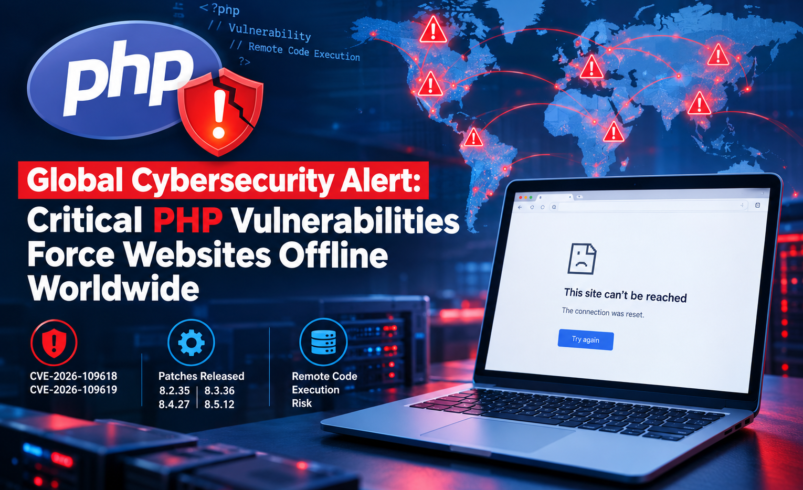
The PHP security team released fixes on October 21, 2026, for two critical vulnerabilities identified as CVE-2026-109618 and CVE-2026-109619. Both have been rated 9.2 on the CVSS v4.0 severity scale, indicating a critical security risk.
According to CERT-EU, the vulnerabilities could allow attackers to execute malicious code remotely on affected servers without authenticating first. Depending on the environment, a successful attack could expose sensitive information, compromise a server, or disrupt online services.
The flaws have been associated with the name PHP2Shell in security reporting. Following disclosure, cybersecurity teams began prioritizing updates and assessing systems exposed to the internet.
Reports have documented organizations taking some websites and services offline as a precaution while applying patches and checking their systems. These actions do not necessarily mean every affected organization was hacked; some shutdowns were preventive measures.
Why Are These PHP Vulnerabilities So Serious?
PHP is a server-side programming language that processes requests, interacts with databases, and generates dynamic website content. It is used by many websites and content management systems, including WordPress-based websites.
A vulnerability in the PHP runtime can be particularly concerning because it may affect the underlying server environment rather than a single website feature or plugin.
The two reported vulnerabilities involve problems with memory handling and internal request state. Under certain conditions, these flaws may enable remote code execution, potentially allowing an attacker to run unauthorized code on a vulnerable server.
Potential consequences include:
Website disruption: Attackers may interfere with normal website operations.
Sensitive data exposure: Information stored or processed by an affected server could be at risk.
Server compromise: Successful remote code execution may give an attacker a path to deeper system access.
Business interruption: Organizations may temporarily disable services while applying security fixes.
Customer trust concerns: A compromised website can damage a business’s reputation and customer confidence.
The actual impact depends on the affected PHP version, server configuration, and whether a system has been patched or otherwise protected.
Which Websites and Servers Could Be Affected?
The risk extends to internet-facing systems running vulnerable PHP versions. CERT-EU identifies environments including PHP-FPM, Apache with mod_php, PHP-CGI, FrankenPHP, and LiteSpeed among the potentially affected setups.
Websites using WordPress and other PHP-based platforms should not assume they are safe simply because their themes, plugins, or content management systems are up to date. The server’s PHP runtime also needs to be checked.
Organizations should review:
WordPress websites and other PHP-based content management systems.
E-commerce websites and online booking platforms.
Hosting servers and web applications.
Government, education, healthcare, and business websites.
Third-party software or appliances that bundle PHP internally.
Not every PHP installation is necessarily vulnerable. Website owners should confirm their installed version and the relevant vendor guidance before deciding what action is required.
Which PHP Versions Include the Security Fixes?
CERT-EU lists the following PHP releases as containing fixes for the two vulnerabilities:
PHP branch
Fixed version
PHP 8.5
8.5.12
PHP 8.4
8.4.27
PHP 8.3
8.3.36
PHP 8.2
8.2.35
Source: CERT-EU Security Advisory 2026-018.
Website administrators should confirm the appropriate update with their hosting provider or operating-system vendor. Organizations using older or unsupported PHP branches should seek vendor-specific guidance rather than assuming that upgrading to one of the listed versions is directly possible.
What Should Website Owners Do Immediately?
Website owners and administrators should treat this alert as a priority and follow a structured security response.
1. Check the PHP Version
Review the PHP version configured for every website and application. On hosting platforms, this information may be available through the hosting control panel or server management tools.
For WordPress sites, check the PHP environment through the hosting dashboard or the site’s health information. Do not publish sensitive server configuration details publicly.
2. Apply the Security Update
Install the appropriate patched PHP release as soon as possible. If PHP is managed by the hosting provider, contact support and request confirmation that the affected runtime has been updated.
Updating WordPress core or individual plugins alone does not necessarily fix a vulnerability in the PHP runtime.
3. Temporarily Isolate Systems That Cannot Be Patched
If a vulnerable, internet-facing system cannot be secured promptly, follow official cybersecurity guidance on restricting public access or taking it offline until remediation is complete. This can help reduce exposure while the necessary fix is applied.
4. Review Logs for Suspicious Activity
Check web server, PHP, firewall, and security monitoring logs for unusual requests, unexpected errors, suspicious file changes, or other signs of compromise.
Patching is essential, but it does not automatically establish that a server has not already been attacked.
5. Scan for Signs of Compromise
Review recently modified files, administrator accounts, scheduled tasks, and unexpected processes. If compromise is suspected, follow an incident-response process and involve a qualified security professional.
Preserve relevant logs and evidence before making major changes where possible.
6. Check Backups and Recovery Plans
Ensure that clean, recent backups are available and that restoration procedures have been tested. Backups are especially important if a website must be rebuilt or restored following a security incident.
7. Monitor Official Security Advisories
Continue monitoring the official PHP security announcements, hosting-provider notices, and relevant national cybersecurity advisories for additional fixes or updated recommendations.
How Can WordPress Website Owners Reduce the Risk?
Because WordPress runs on PHP, site administrators should check both the website software and the underlying hosting environment.
Recommended precautions include:
Update PHP to a compatible, patched version.
Update WordPress core, themes, and plugins.
Remove unused themes and plugins.
Use strong administrator passwords and multi-factor authentication.
Keep regular off-site backups.
Use a web application firewall where appropriate.
Review administrator accounts and file changes.
Avoid displaying detailed PHP errors on public pages.
Contact the hosting provider if server-level updates are managed externally.
A security plugin or firewall can add another layer of protection, but it should not be treated as a replacement for the official PHP security fix.
Will the PHP Vulnerabilities Affect Every Website?
No. The alert does not mean every website worldwide is compromised or must be shut down.
The vulnerabilities concern affected PHP environments, and the actual exposure depends on the software version, configuration, hosting setup, and whether the relevant security update has been applied. Some organizations may take precautionary measures even when there is no confirmed evidence of a breach.
Website owners should verify their own infrastructure rather than relying on broad claims about the percentage of websites affected.
Conclusion
The PHP2Shell security alert highlights how a vulnerability in widely used infrastructure software can create risks across many different websites and online services. The reported flaws can potentially enable unauthenticated remote code execution, making prompt remediation essential.
Website owners should verify their PHP versions, apply the relevant security updates, investigate suspicious activity, and isolate systems that cannot be secured promptly. For WordPress users, checking the hosting environment is just as important as updating themes and plugins.
The most important step is to act on verified security guidance rather than wait for an outage or evidence of a successful attack.
Frequently Asked Questions
1. What is the PHP2Shell security alert?
PHP2Shell is a name used in reporting about two critical PHP vulnerabilities, CVE-2026-109618 and CVE-2026-109619, which can potentially allow unauthenticated remote code execution on vulnerable systems.
2. Why are some websites going offline?
Some organizations have temporarily restricted access to vulnerable systems while applying security updates or checking their infrastructure. A precautionary shutdown does not necessarily mean a website has been hacked.
3. Does this vulnerability affect WordPress websites?
WordPress runs on PHP, so websites using vulnerable PHP runtimes should assess their exposure. Updating WordPress alone may not fix a vulnerability in the underlying PHP version.
4. What should I do if my website uses PHP?
Check the installed PHP version, contact your hosting provider if necessary, install the appropriate security update, and review logs for suspicious activity. If the system cannot be secured promptly, follow official advice on restricting access.
5. Can a security plugin fix the PHP vulnerability?
A security plugin or web application firewall may provide additional protection, depending on its capabilities and configuration. However, it should not replace updating PHP to a patched version.
6. Where can I find reliable updates?
Check the official PHP security announcements and guidance from recognized cybersecurity agencies such as CERT-EU and the US National Security Agency.